 QuantumReady

An honest picture, without an enterprise programme
You have a handful of applications, a cloud account, a few dozen certificates and no dedicated cryptography team. What you need is an honest picture and a short list, not a platform deployment and a professional services engagement.
Three things, in this order
What is exposed today
A real TLS handshake against your domain tells you whether your edge negotiates a post-quantum hybrid key exchange. No agent, no signup, no access to your systems.
What is in your code
A public repository scan shows the report format and the findings on code that is already public. When you are ready, a plan opens your private repositories.
What to fix first
The report ends with a prioritised action list, not a wall of findings. That list is the thing you take to your team on Monday.
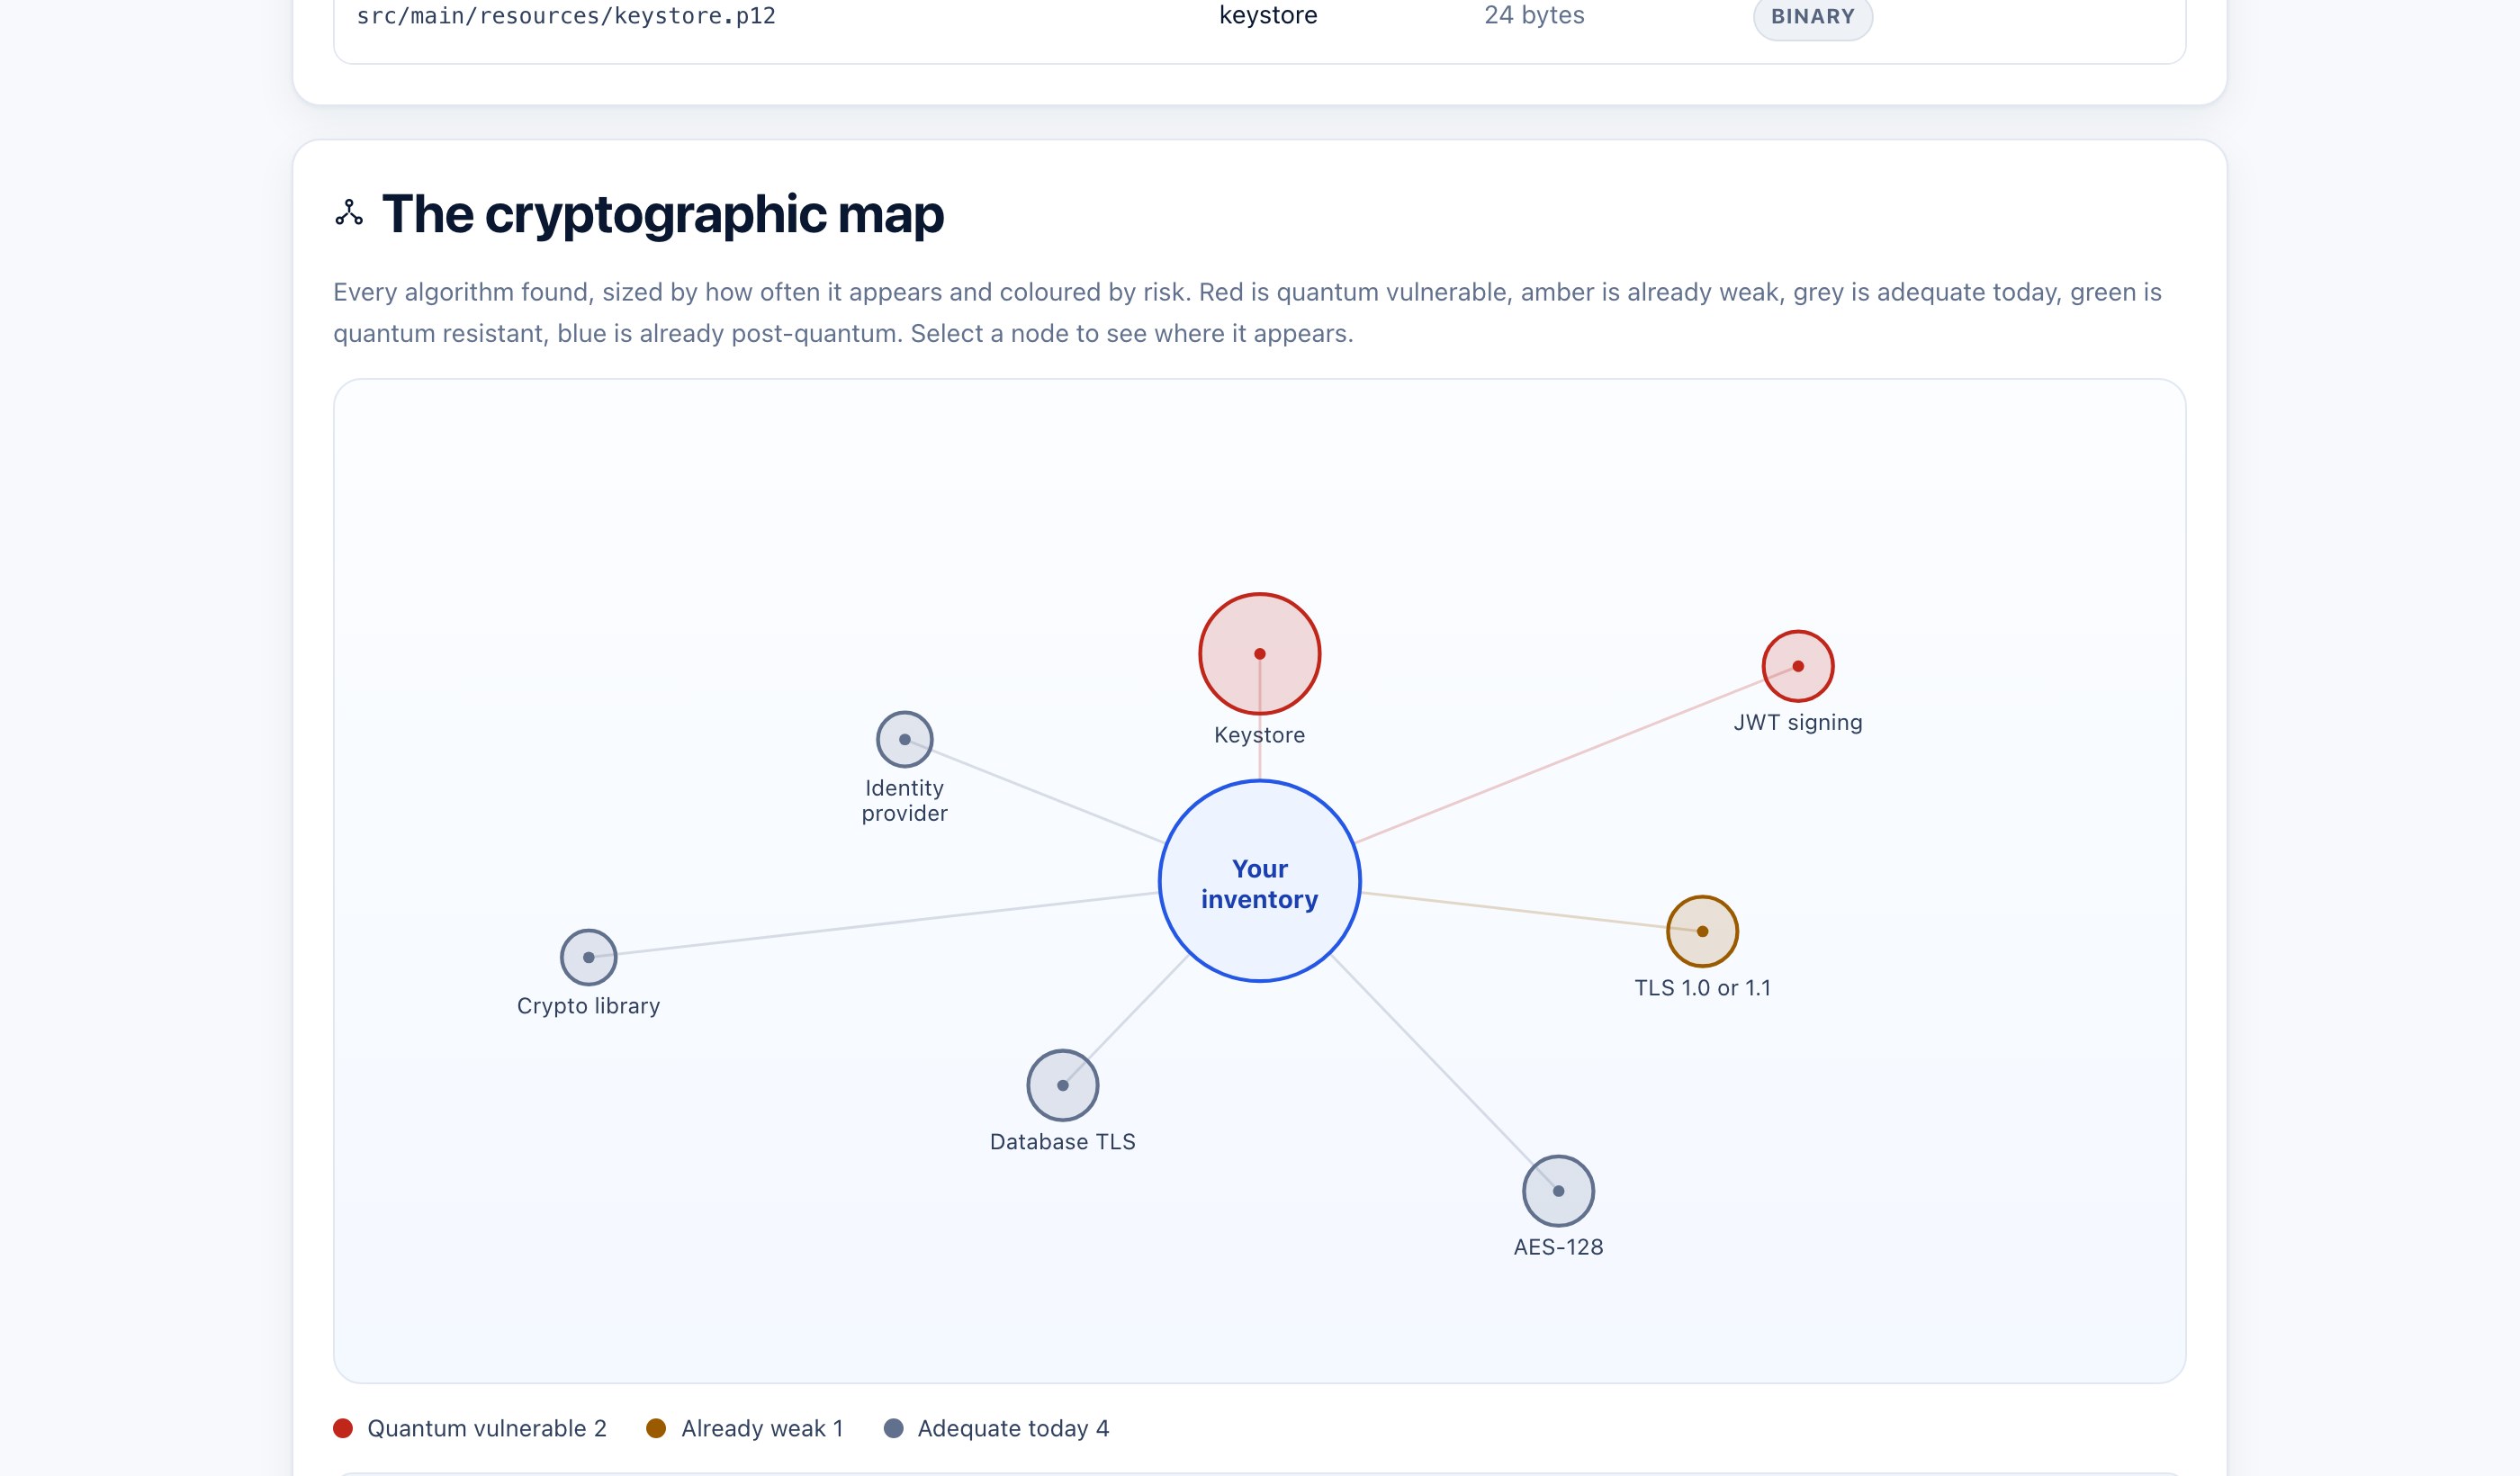
The cryptographic map from a free scan: every algorithm found, sized by frequency and coloured by risk.
Nothing to start. S$299 a month when you need your own code.
The free tier is not a trial, and the paid tier is not a programme. If you only ever need the public scan, you never pay.
| Free | Team | |
|---|---|---|
| Public endpoint and repository scans | Unlimited | Unlimited |
| Private repositories | Not included | 10 |
| Report retention | 24 hours | 365 days |
| Shareable report links | Not included | Yes |
| Offline runner seats | 1 | 5 |
| Price | S$0 | S$299 per month |
What it will not do
It will not tell you that you are compliant, and it will not replace a security review. It reports technical evidence and tells you exactly what it could not see. If that sounds like a limitation, it is: it is also the reason the report is worth attaching to a customer questionnaire.