The report you can send
A finalized PQC readiness report: the scope, the cryptographic inventory, every finding with its evidence, the prioritised actions, and the coverage statement. One document for a customer, an auditor or a board — not a dashboard screenshot.
 QuantumReady
Cryptographic discovery and migration evidence
REPORT
Eight sections, in the order a reviewer reads them
The same structure on every report, so a customer or an auditor learns it once.
1. Executive summary
The score, the counts by risk, and the three things that matter, on one page.
2. Scope and coverage
What was read, what was skipped, and the budget the scan worked within.
3. Cryptographic inventory
Algorithm, key length, system, owner and the evidence behind each row.
4. Findings by risk
Quantum vulnerable, deprecated, adequate, resistant, post-quantum ready.
5. Prioritised actions
What to change first, with the recommended replacement for each algorithm.
6. Migration waves
The work sequenced against the CSA dates, with owners and target dates.
7. Evidence appendix
The file, line and matched excerpt behind every material finding.
8. Coverage limits
A plain statement of what this scan could not see, so nobody reads silence as safety.
Exports
PDF for the reader, JSON and CSV for your records, CycloneDX CBOM for your tooling.
The same engine, the same format
The sample below is produced by the product, not designed for the website. Nothing in it is yours, and there is nothing to sign in for.
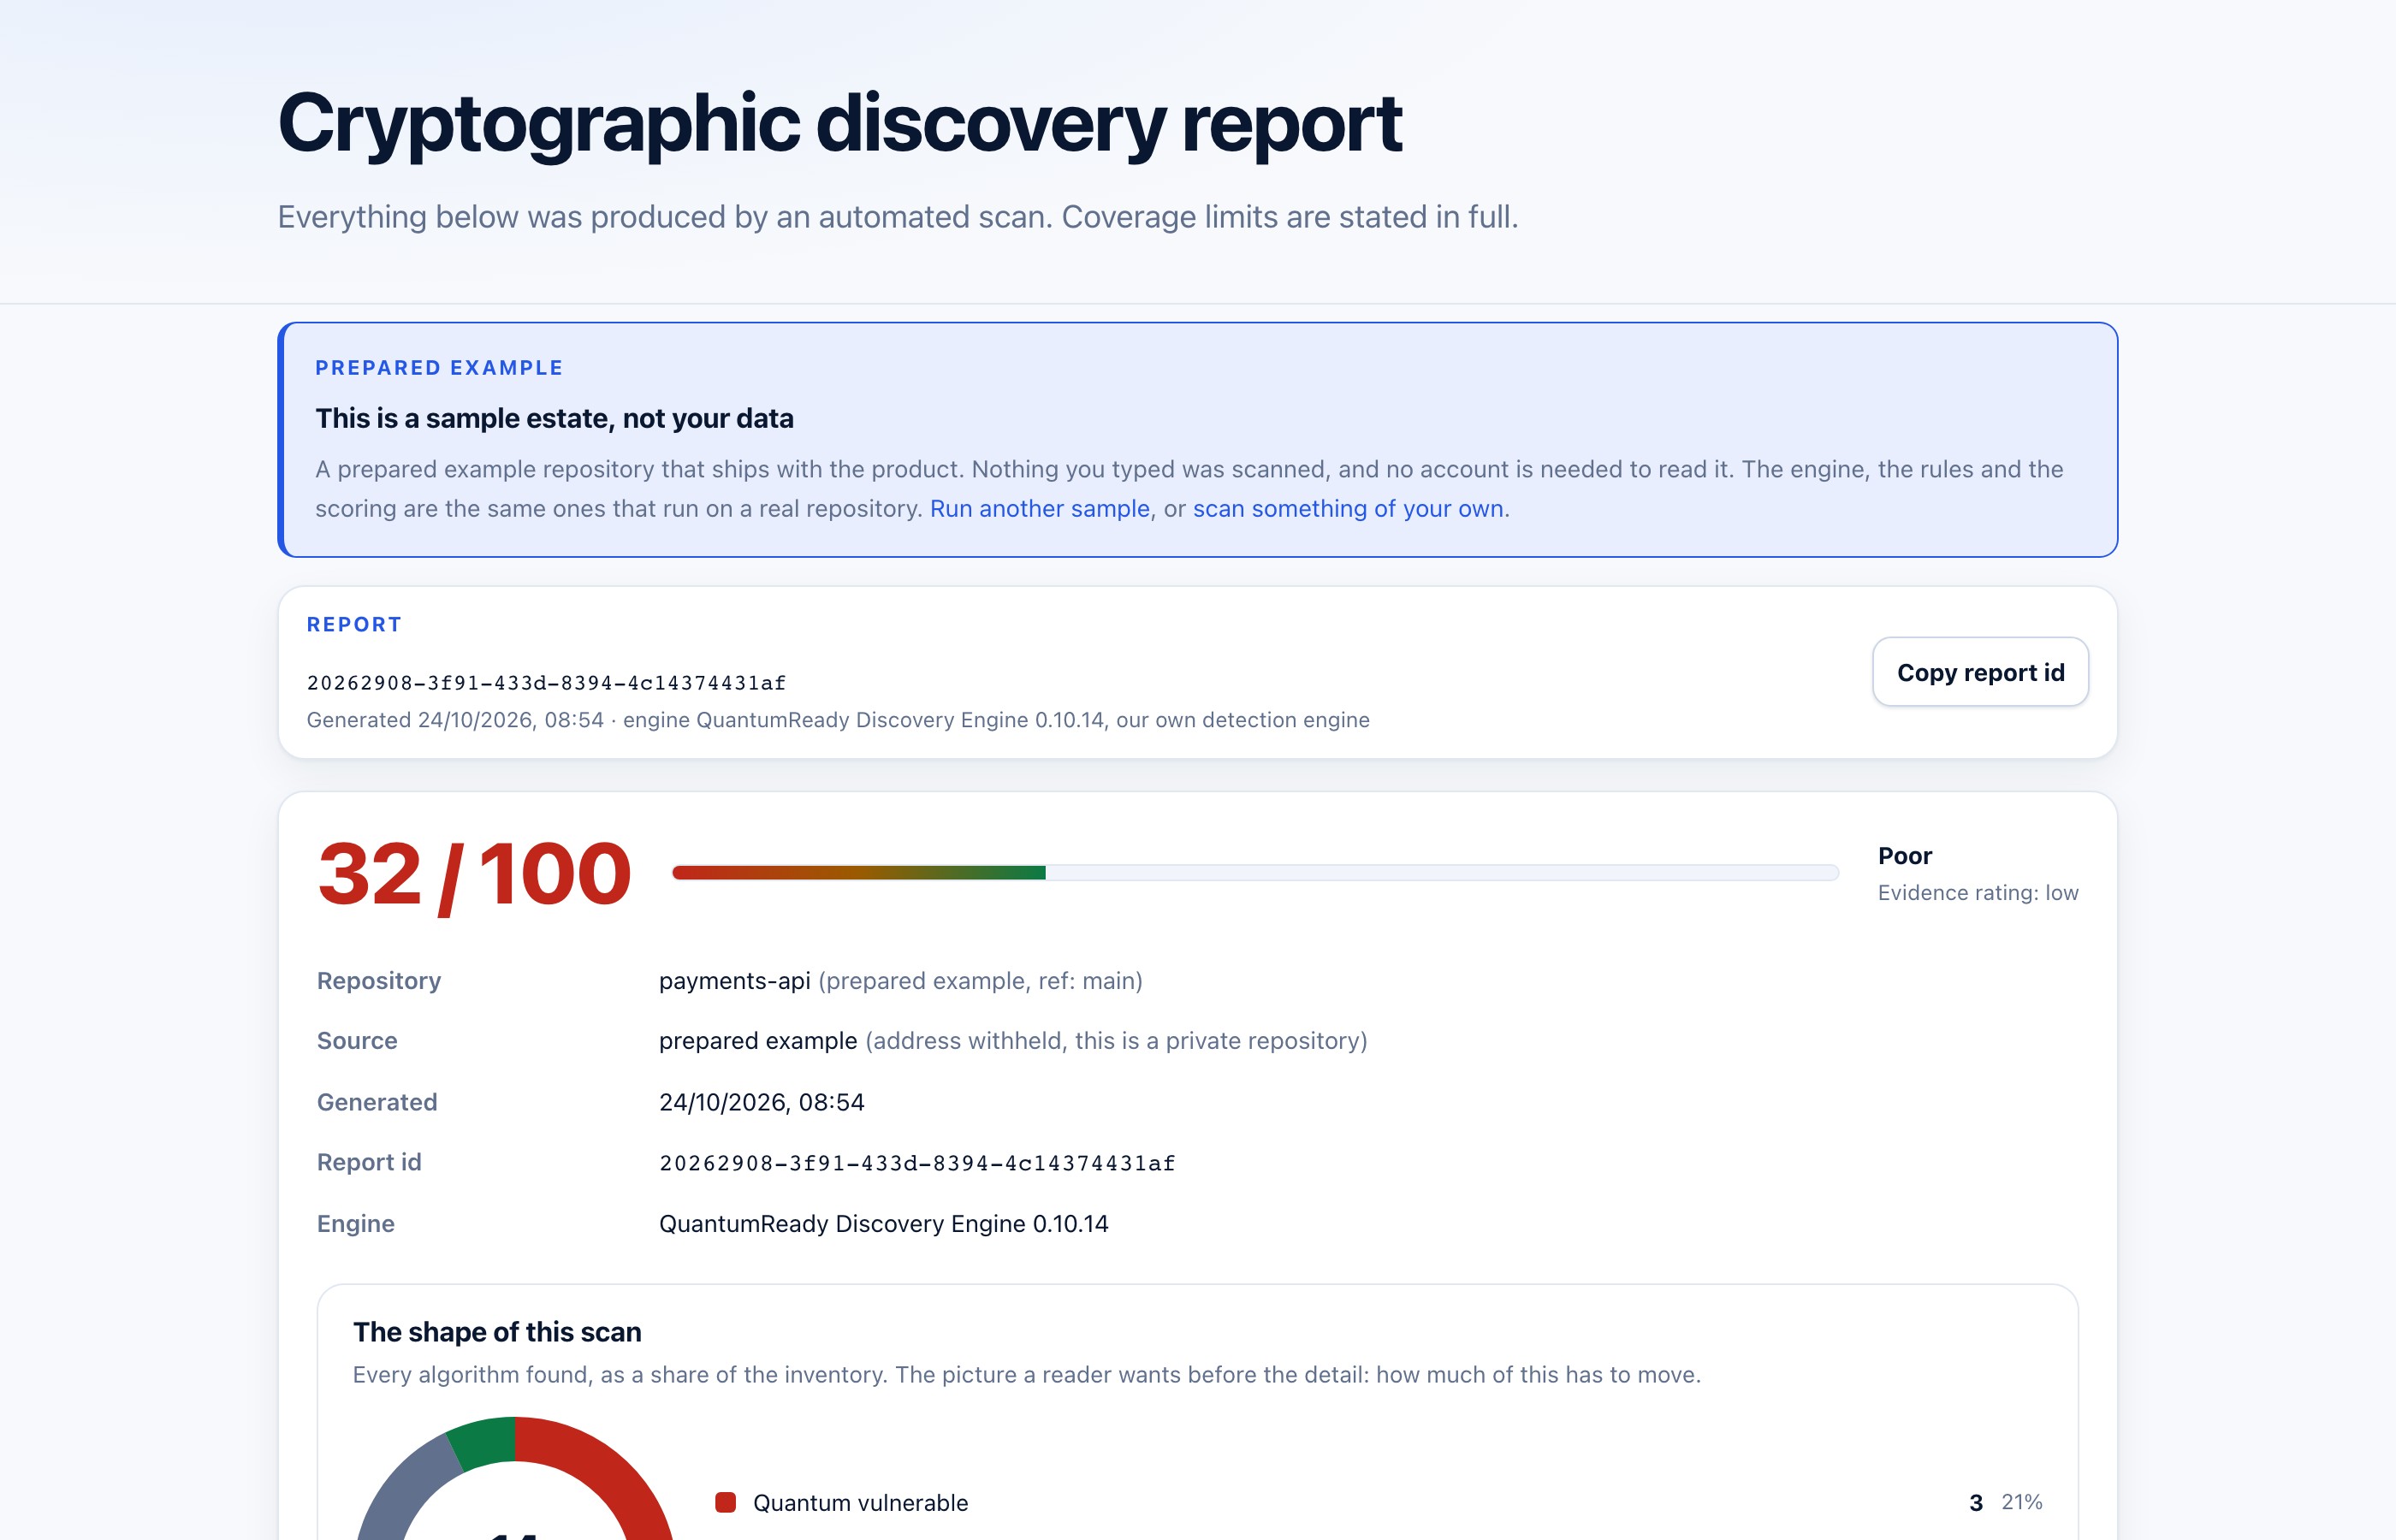
A prepared example from the product. Coverage limits are stated in full.
What it is, and what it is not
It is technical evidence with a stated boundary: what was read, what was found, what to change first, and what the scan could not see. It is the document a customer's security team or an auditor asks you for.
It is not a certificate, and it does not make you compliant. Compliance also needs attestation, documentation and human review, and those remain yours. If a reviewer wants a person to have checked every material finding before it is sent, that review is available as a separate step.
Three readers, one document
A customer
A bank or an agency sends a cryptography questionnaire. Attach the report instead of writing paragraphs.
An auditor
The inventory, the owner of each fix, the wave and the date, with the coverage boundary attached.
A board
A one-page summary of exposure and sequence, generated from the same register rather than retyped.